“Research Report: Automatic Schema Inference From Unknown Protobuf Messages”, by Jared Chandler, addresses a challenge in protocol reverse engineering. Packed binary formats are widely used in enterprise software, mobile applications, and IoT devices, but they typically aren’t structured in a user-friendly way. Protobuf, one of the most popular of these formats, includes field numbers and datatypes in each message. Unfortunately for humans, however, it omits the complete schema needed to interpret it. Determining which fields are required, which are optional, and which can be repeated still demands attention to detail, specialized expertise, and ample time from a (manual) human analyst.
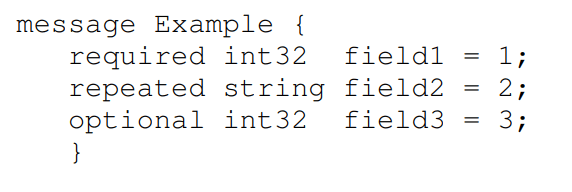
integer, a variable number of strings, and an optional 32-bit integer.
The author closes this gap with FUBOTORP, a tool that automatically infers protobuf schemas from a collection of raw binary messages. By observing the presence, absence, and repetition of each field across messages, FUBOTORP identifies field arity constraints and reports them as a complete protobuf schema, recursing into nested subformats (as necessary) along the way. In evaluation, the approach achieved high accuracy across a variety of inputs, perfect accuracy given at least 10 sample messages, and produced schemas consistent with four real-world datasets.
To learn more, read the paper:
Chandler, J. Research Report: Automatic Schema Inference From Unknown Protobuf Messages. IEEE Security and Privacy Workshops (SPW), May 2025. DOI: 10.1109/SPW67851.2025.00013
To be notified about more SPLICE news, subscribe to this blog!




Leave a Reply