“AgenTEE: Confidential LLM Agent Execution on Edge Devices”, by Sina Abdollahi et al., addresses a security gap present in locally-hosted AI agents. LLM agents offer powerful automation capabilities, but their integration with non-deterministic models and third-party services exposes them to more potential attacks than conventional applications. In pursuit of stronger user privacy (and lower latency), it has become favorable to pull LLM deployments from the cloud and execute them directly on “edge devices”. However, secure hosting of these complicated LLM agent pipelines remains a challenge; deployments must protect proprietary assets and sensitive runtime states on heterogeneous platforms that are vulnerable to software attacks and potentially controlled by malicious users.
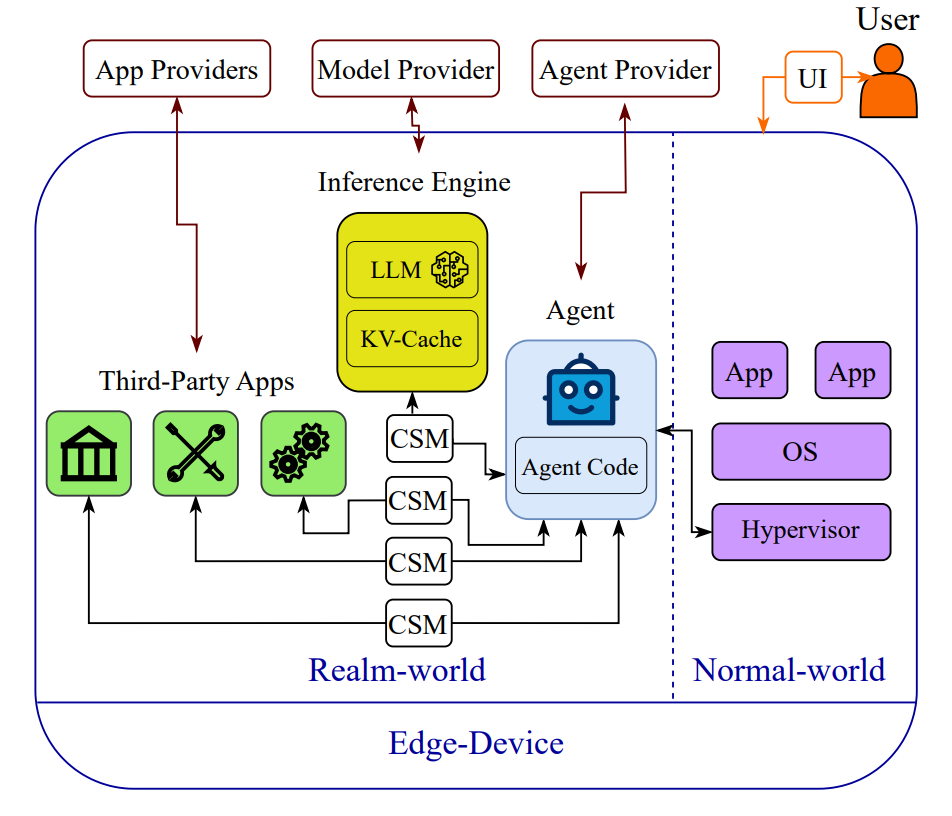
The authors close this security gap with AgenTEE, a system for deploying confidential agent pipelines on edge devices. AgenTEE places the agent runtime, the inference engine, and third-party applications into independently-attested confidential virtual machines (cVMs), and mediates all interaction between them through explicit, verifiable communication channels. Built on Arm Confidential Compute Architecture (CCA), the system enforces ironclad system-level isolation of sensitive assets and runtime state.
To learn more, read the paper. To receive notification of SPLICE news, subscribe to this blog!
Abdollahi, S., Maheri, M. M., Forough, J., Al Sadi, A., Millar, J., Kotz, D., Kogias, M., & Haddadi, H. (2026). AgenTEE: Confidential LLM Agent Execution on Edge Devices. Proceedings of the Sixth European Workshop on Machine Learning and Systems (EuroMLSys ’26), 473-480. https://doi.org/10.1145/3805621.3807660




Leave a comment